AI-powered penetration testing
Elite pentesting
at the speed of AI.
Ambit finds, exploits and validates the vulnerabilities in your web apps and APIs, the way a real attacker would. One simple platform, run by AI and led by OSCP/OSWE/OSEE-certified testers. Audit-ready reports in days, not weeks.
Results in days. Retest included. Auditor-accepted, or your money back.
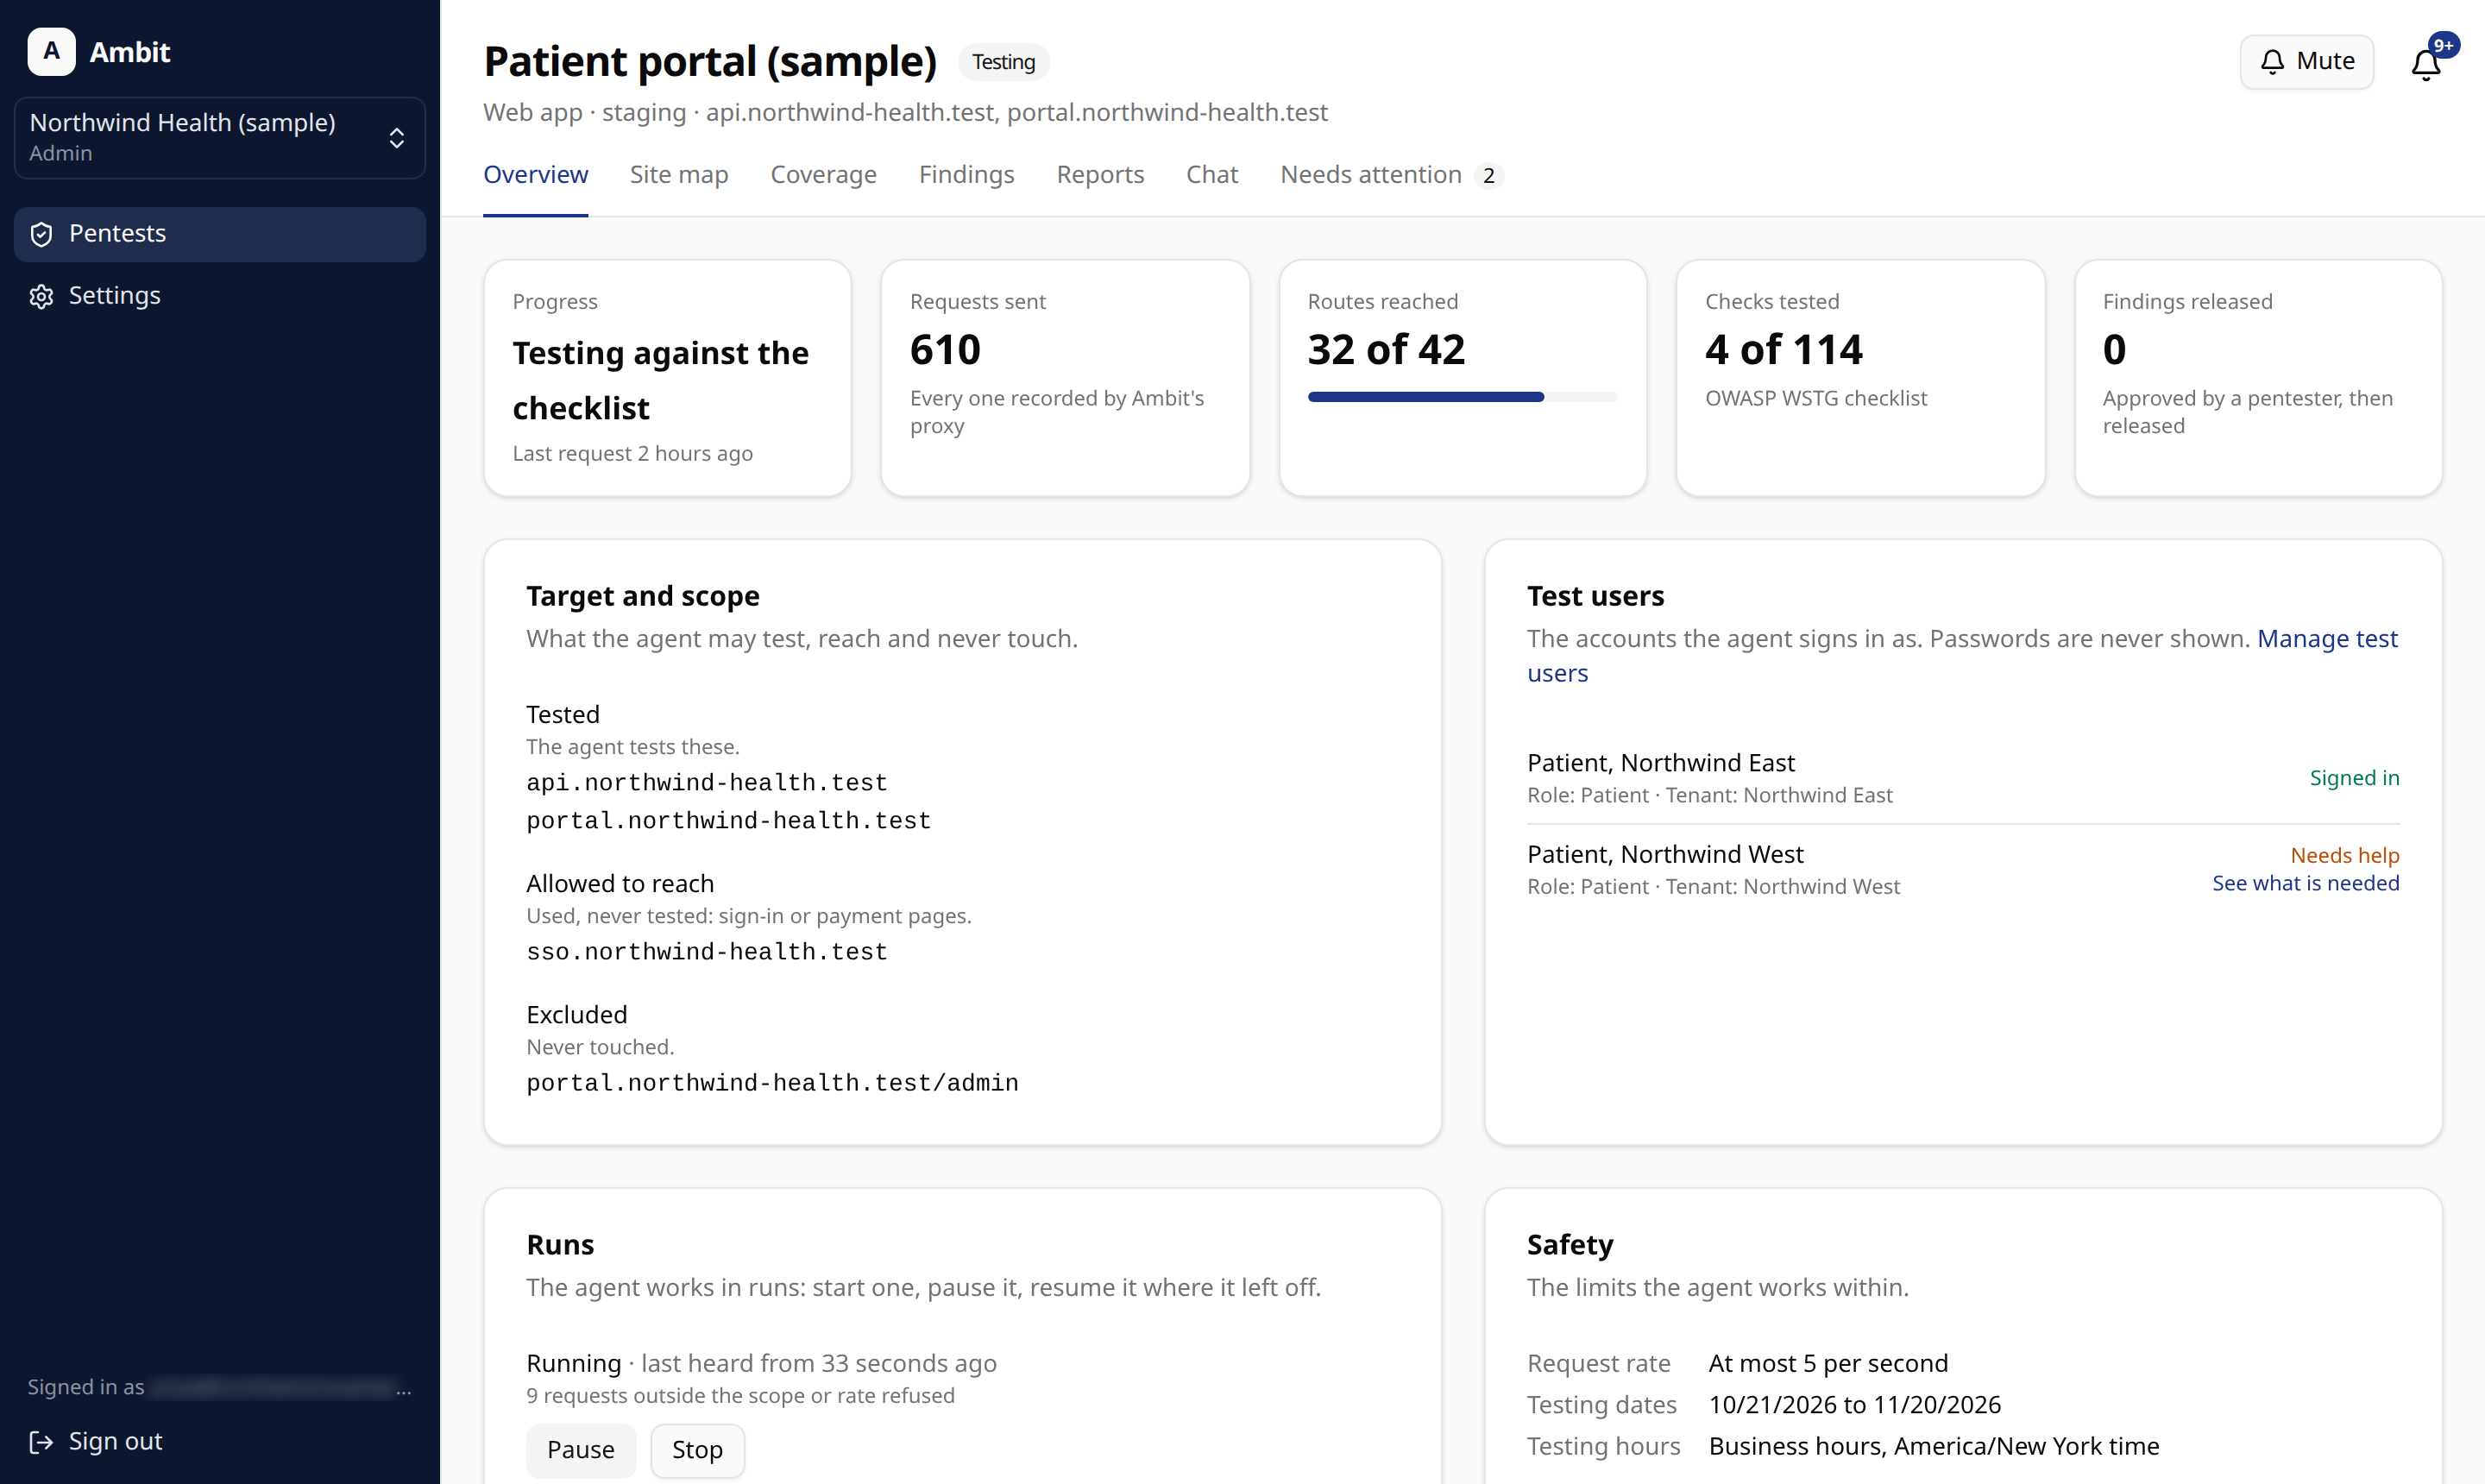
A sample pentest in Ambit: scoped, now testing, with 71 of 114 test cases run, three findings so far, and the agent asking the customer whether to check another endpoint.
- companies tested by our team
- 150+
- vulnerabilities found across bug bounties, disclosure programs and client engagements
- 500+
A real pentest, not a scan
See your app the way an attacker does.
A scanner lists what might be wrong. A pentest shows what an attacker can actually do: which weaknesses are real, how they chain together, and how far they lead. That's what Ambit tests, and what your report proves.
Real exploits, not theoretical risk.
A scanner hands you a list of maybes. Ambit attacks each one inside your scope and keeps only what it can prove, with the requests that prove it. The rest is ruled out, not left for you to triage.
How weaknesses chain together.
A pentest follows one foothold as far as it goes. In the sample engagement, one patient's session and one unchecked route reached every clinic's lab results. Your report shows the whole path, and what held.
Fixes your developers can act on.
Every finding comes with its impact, its evidence and a specific fix. Ship the fix and the retest proves it, then your report and attestation letter are updated for your auditor.
Why Ambit
Depth, trust and speed, in one pentest.
Depth
Tested the way an attacker works, not the way a scanner does.
- Every role and tenant you give us, on every route the agent maps
- All 114 OWASP WSTG test cases
- OWASP Top 10 and API Security Top 10, mapped to ASVS
Trust
People who sign their work, and an agent that stays in bounds.
- Led by OSCP/OSWE/OSEE-certified testers
- Every report reviewed and signed, with a reference anyone can verify
- Safe by design: verified scope, enforced rate limits, every request logged through Ambit's proxy
Speed
A pentest without the back and forth.
- One simple platform for scope, live progress, findings and reports
- Results in days, not weeks
- A fixed price, with a retest within 90 days included
How it works
Three steps to a signed pentest.
No kickoff calls, no email threads. Certified testers lead every engagement, and each report is reviewed and signed by one.
-
01
Scope it.
Tell us what to test: your web app or API, a test user per role, and when. Prove you own the domain, confirm the test, done. Nothing to sign.
-
02
We attack it.
Our AI agent, led by certified testers, maps your app and tests it the way a real attacker would. Watch progress live and answer its questions in one place.
-
03
Get proof and a signed report.
Validated vulnerabilities with evidence and fixes, an audit-ready report and attestation letter, and a free retest within 90 days.
Research
We find what scanners miss, in software the world runs on.
Our team has found 500+ vulnerabilities across bug bounties, disclosure programs and client engagements. Our latest research: 78 reported to the maintainers of 31 widely used open-source projects under coordinated disclosure, 1 critical and 33 high, each proved end to end and published once the maintainer has.
- Reported
- 78
- Confirmed by maintainers
- 12
- Published so far
- 1
Published advisory · FileBrowser Quantum · GHSA-c84q-q5g6-r47f
With per-user home folders turned on, an account whose name cleans to nothing or to another user's name gets the wrong home: every user's files, or one victim's. It can read, create and overwrite them.
What you get
A report your auditor can use.
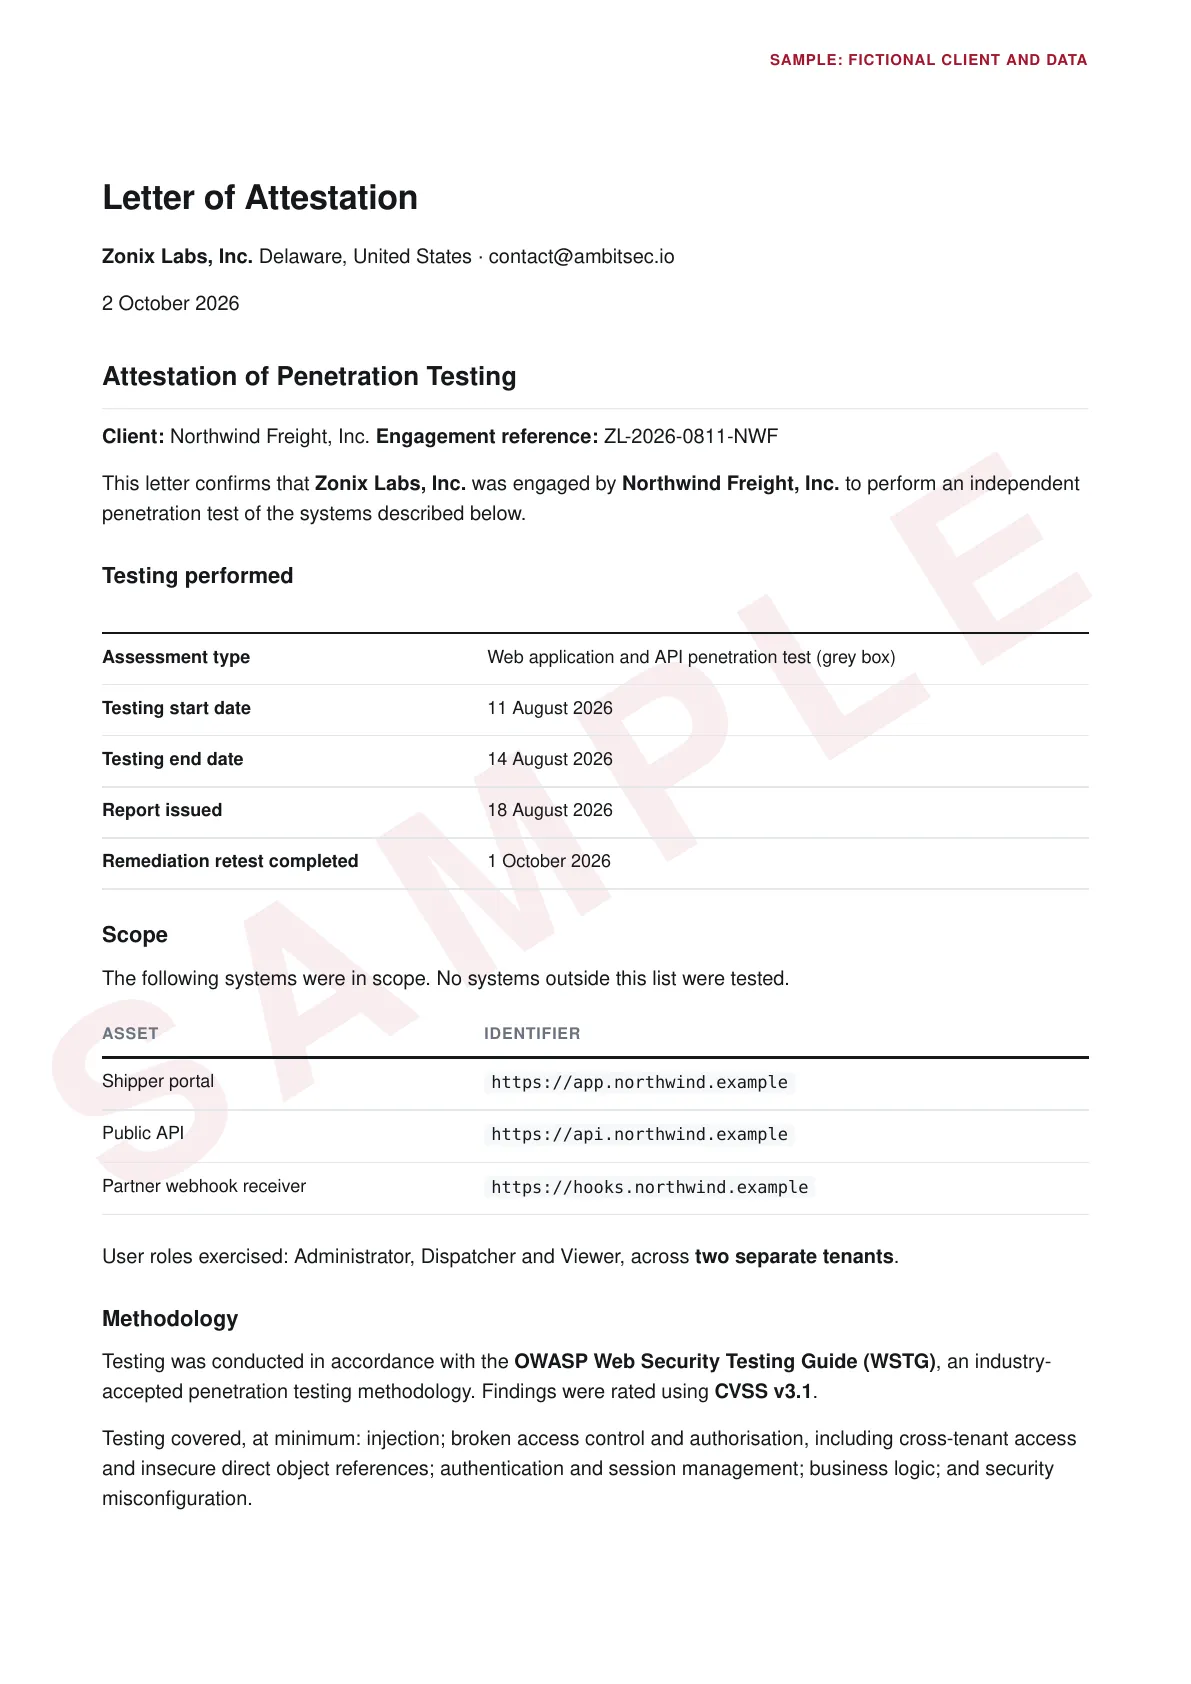
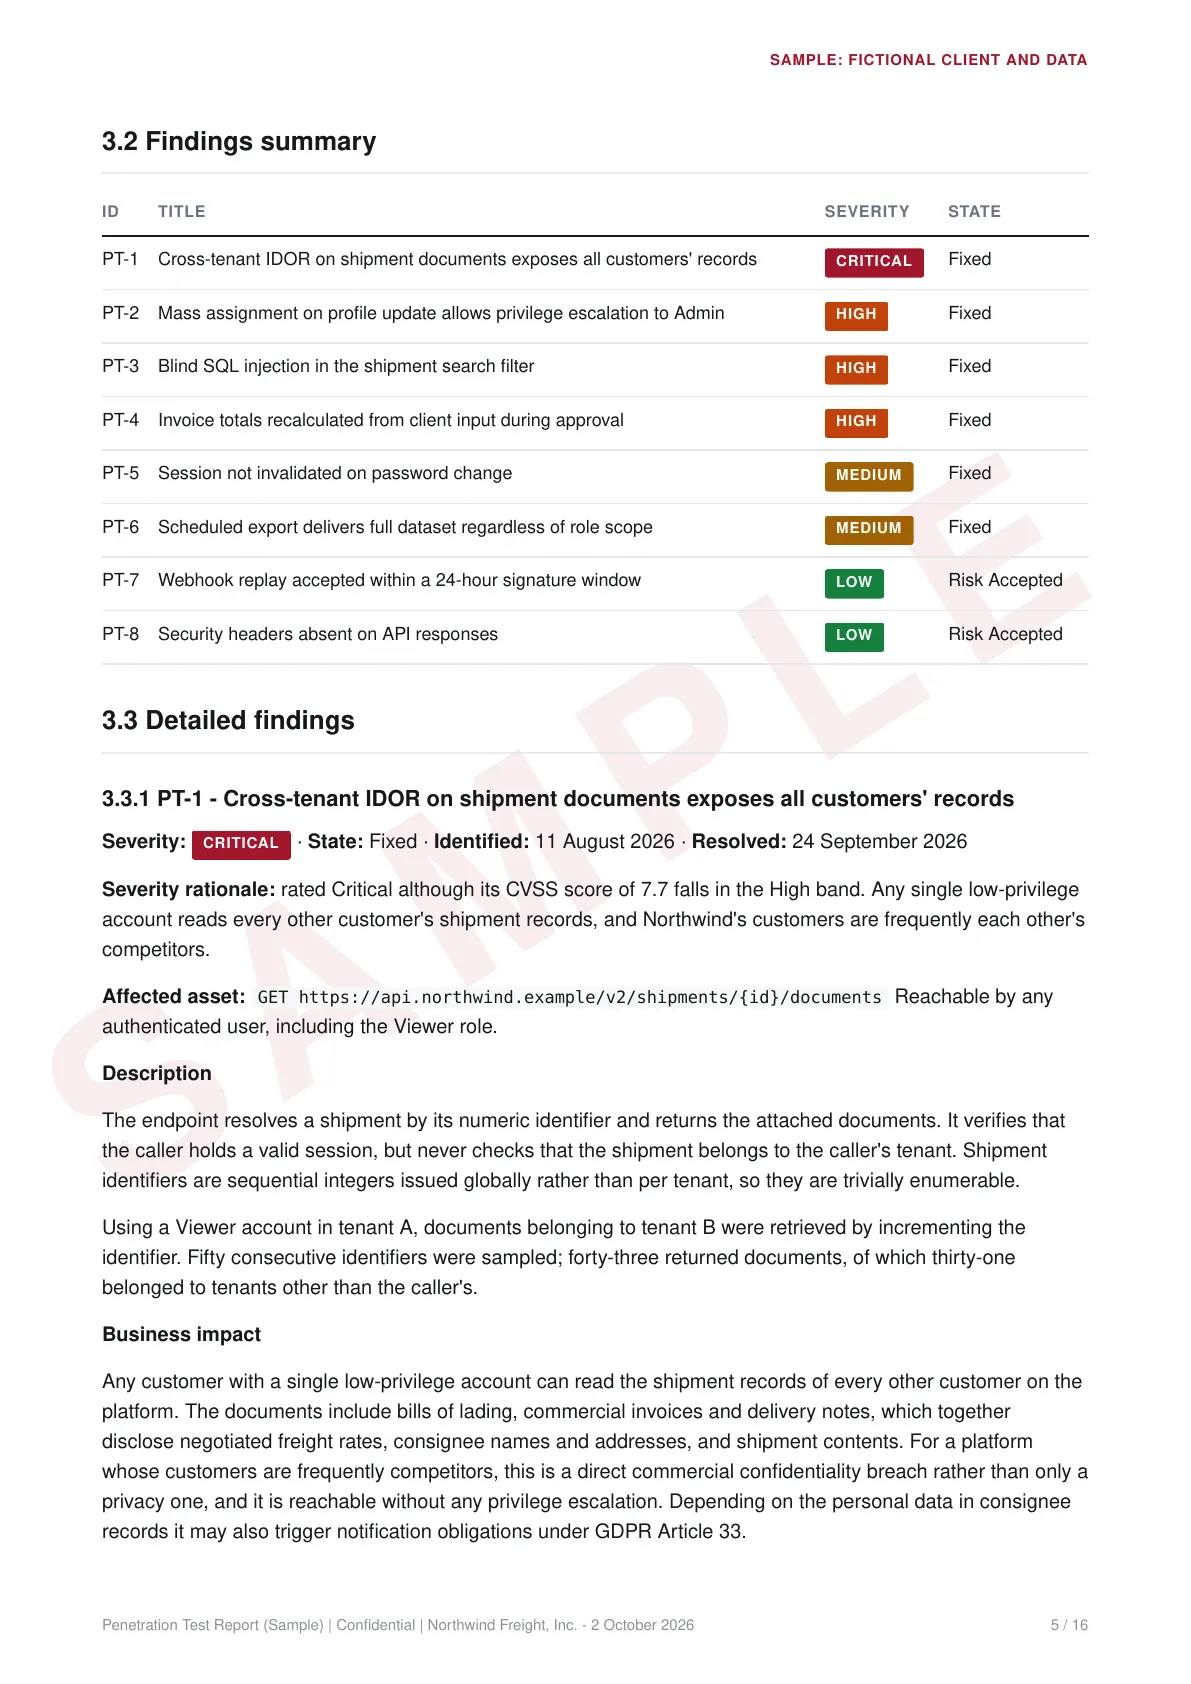
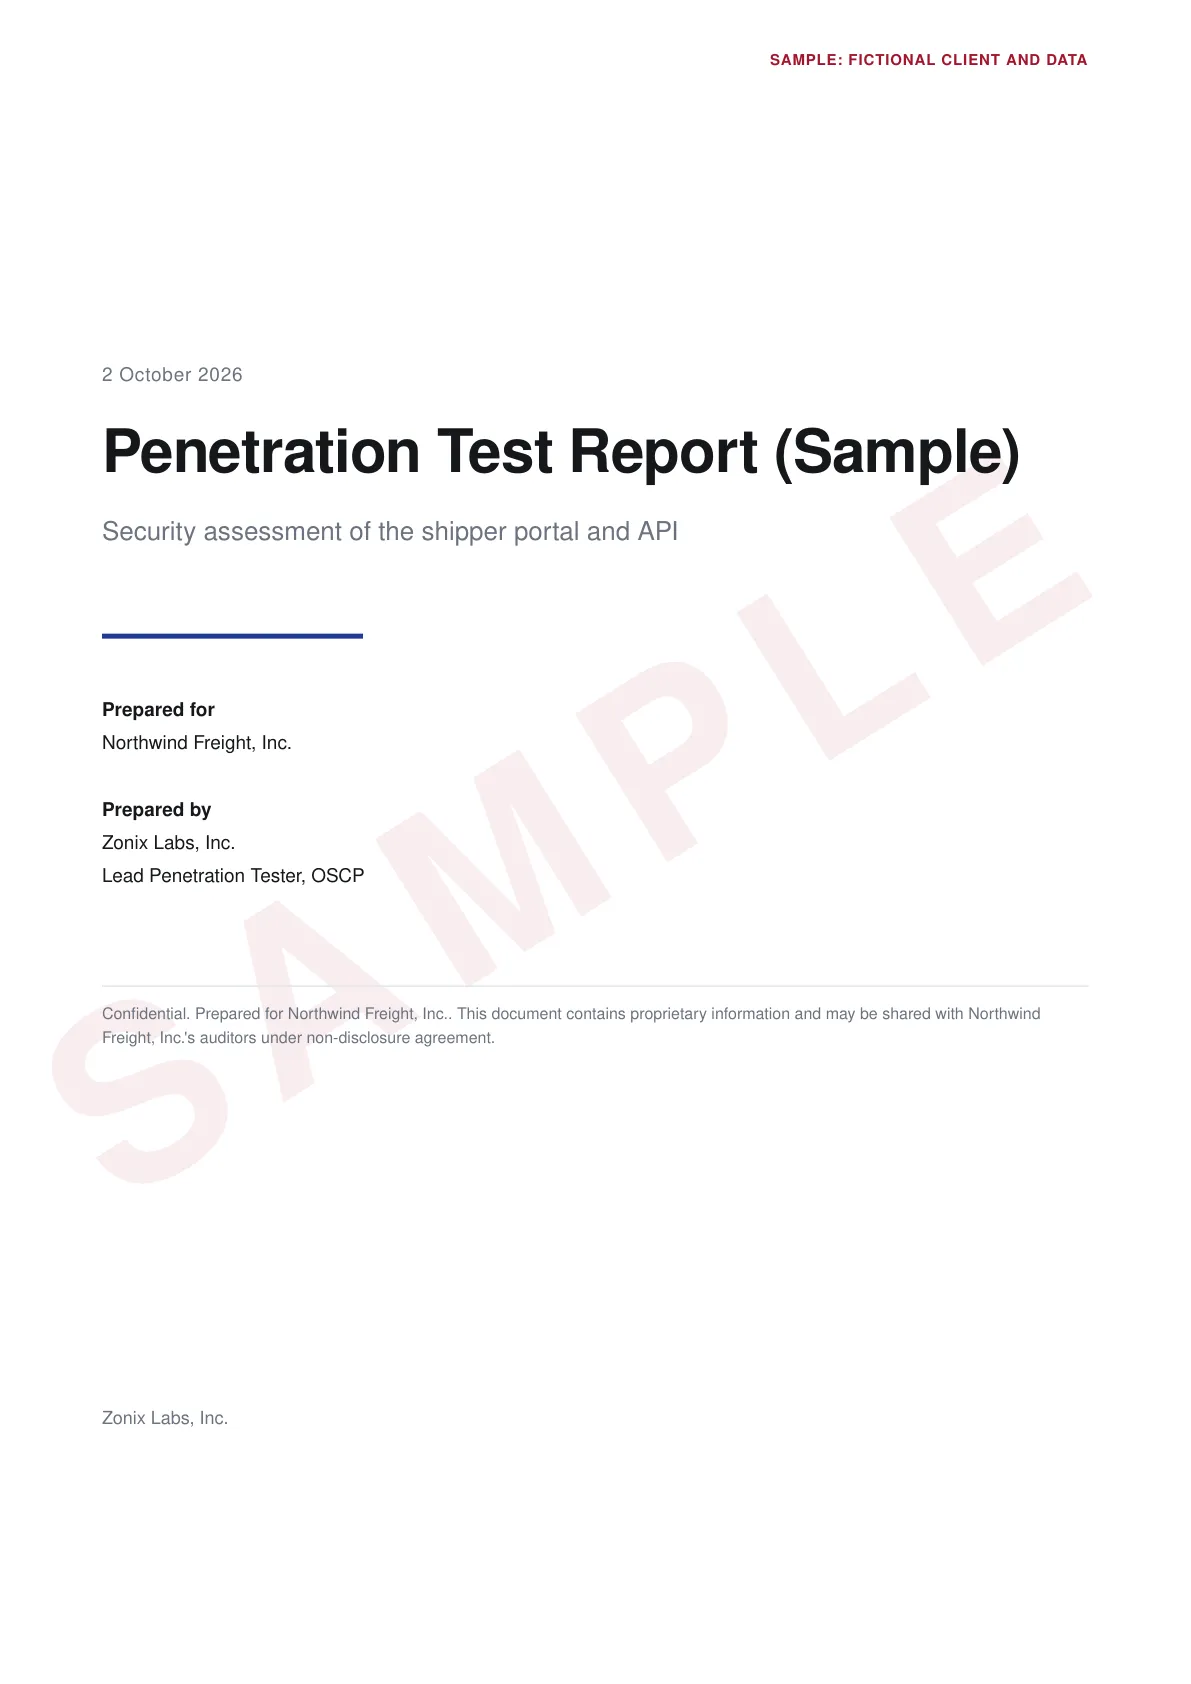
A penetration test report with every finding's CVSS score, evidence and fix, and a signed attestation letter for auditors and customers. Built to be used as evidence for SOC 2 and ISO 27001, and for your customers' security reviews.
- SOC 2
- ISO 27001
Each signed document carries a reference anyone can check at ambitsec.io/verify.
FAQ
Questions buyers ask.
Is this a real pentest, or a vulnerability scan?
A real pentest. A scanner reports what might be wrong. Ambit's agent signs in as your users, attacks your app inside the agreed scope and proves each vulnerability with the requests that exploit it. A certified tester leads the engagement and reviews and signs the report.
Will my auditor accept the report?
Ambit reports are built to be used as evidence for SOC 2, ISO 27001, PCI DSS and HIPAA audits, and for customer security reviews. They state the scope, dates, methodology and tester credentials, and give every finding a CVSS score, evidence and steps to reproduce. Confirm the scope with your auditor before testing. If your auditor won't accept the report as penetration test evidence, we refund the full price or retest at no charge, your choice. Send us their reason in writing. It covers the report, not the outcome of your audit. We don't promise a pass or a certification.
Who are the testers?
OSCP/OSWE/OSEE-certified testers. Our team has tested 150+ companies across finance, cloud infrastructure and SaaS, found 500+ vulnerabilities across bug bounties, disclosure programs and client engagements, and their reports have been accepted in clients' audits. The tester who leads your engagement is named in your report and signs it.
How much does it cost?
$5,000 per pentest, for a web application or an API, with a retest within 90 days included.
Is it safe to run against production?
We recommend a staging copy, but production works. The agent only sends requests to verified, in-scope hosts, at the rate and during the hours you choose. It never load tests, avoids destructive actions and stops to ask when something blocks it. You can pause or stop a run at any time.
What kinds of testing aren't included?
Ambit tests web applications and APIs. Engagements for denial of service, social engineering, physical security and mobile apps are not part of an Ambit pentest.
Do you train AI models on our data?
No. Customer data is never used to train models. Engagement data is deleted 30 days after you accept the final report. Signed deliverables are kept for 6 years so they stay verifiable.
We're a vCISO or compliance firm. Can we offer Ambit to our clients?
Yes: at partner pricing or by referral, with co-branded reports, a partner portal and API, and reports delivered into your clients' Vanta or Drata accounts. The partners page has the details.
More on pricing, the partner program and security and trust.
Get started
What would an attacker find in your app?
Find out in days. Certified testers lead the engagement, and you get a signed report your auditor can use.
Fixed price. Results in days. Retest included.