Sample reports
See exactly what you get, before you buy.
A real penetration test report and attestation letter from Ambit's documents pipeline, about a fictional company. No form, no email: open the PDFs.
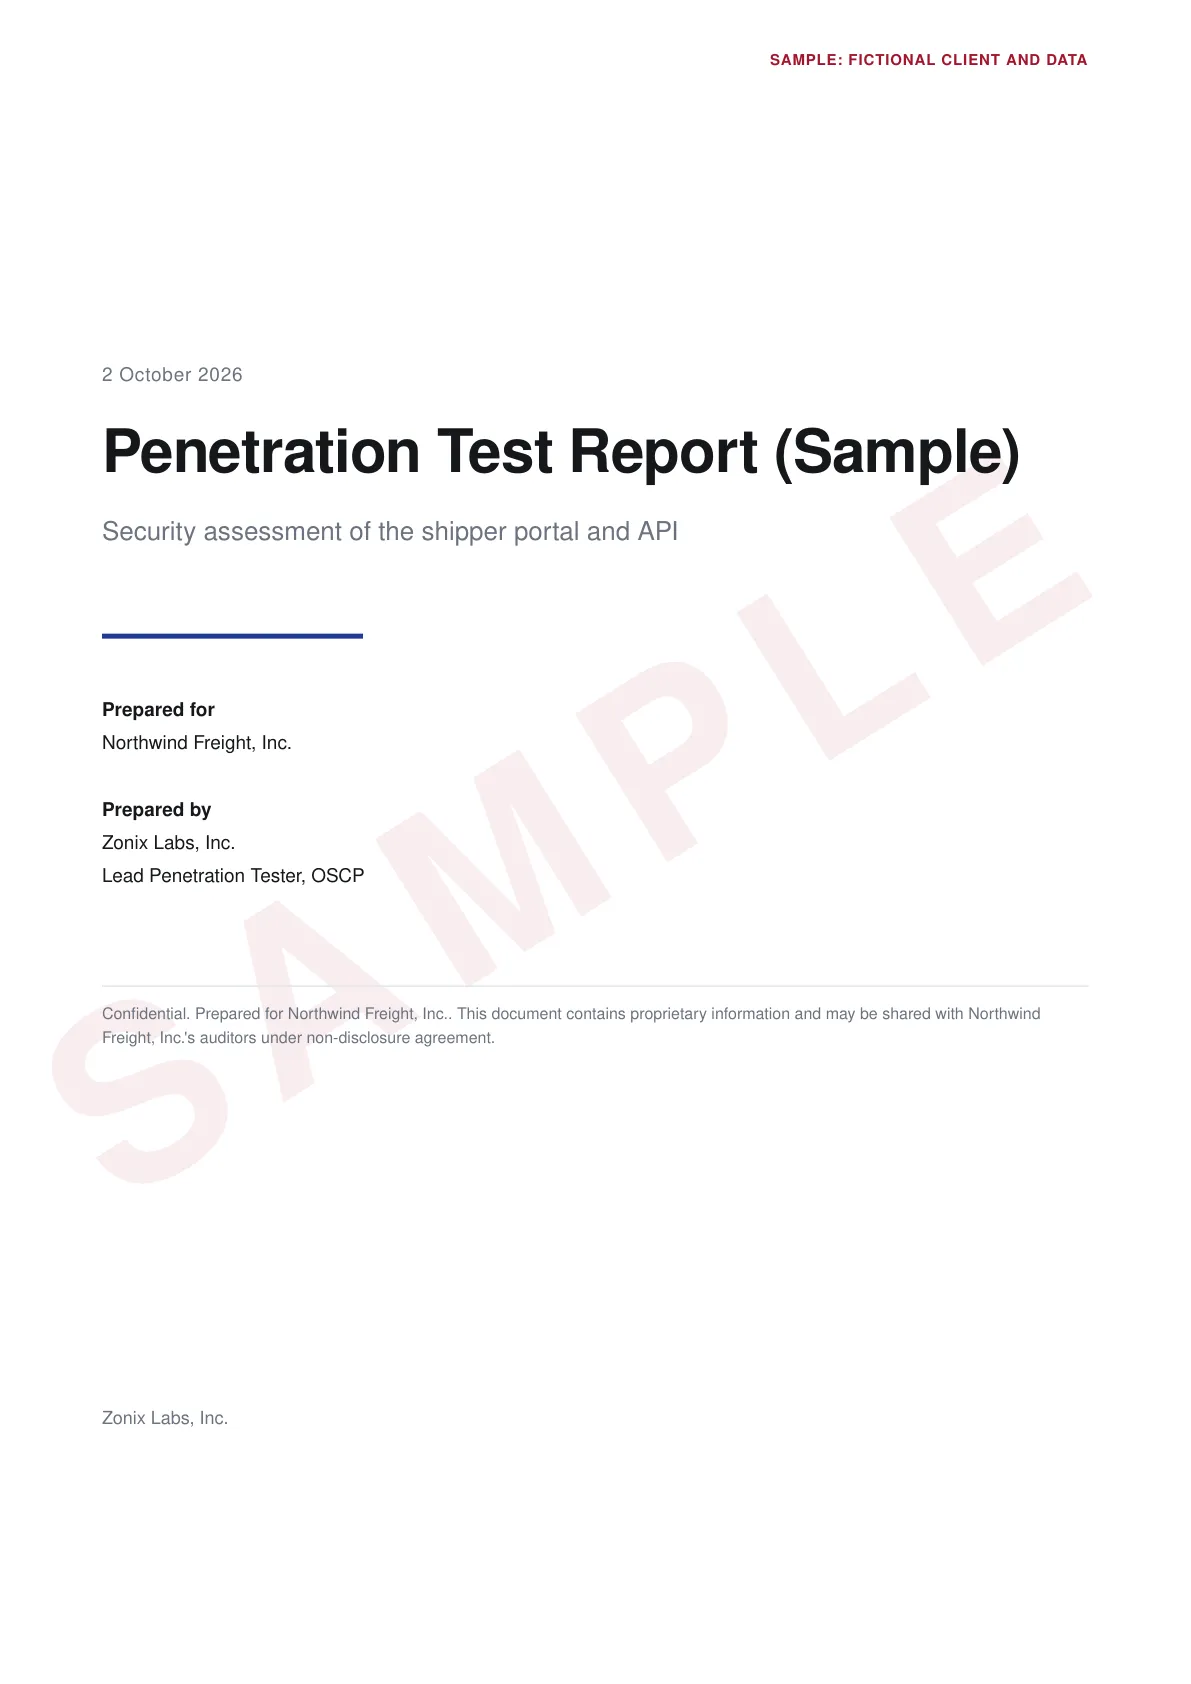
PDF · 16 pages · Sample
Penetration test report
A web app and API test of a fictional freight company: eight findings, from a cross-tenant data leak to missing security headers, each with CVSS, evidence, steps and the retest result.
Open the sample report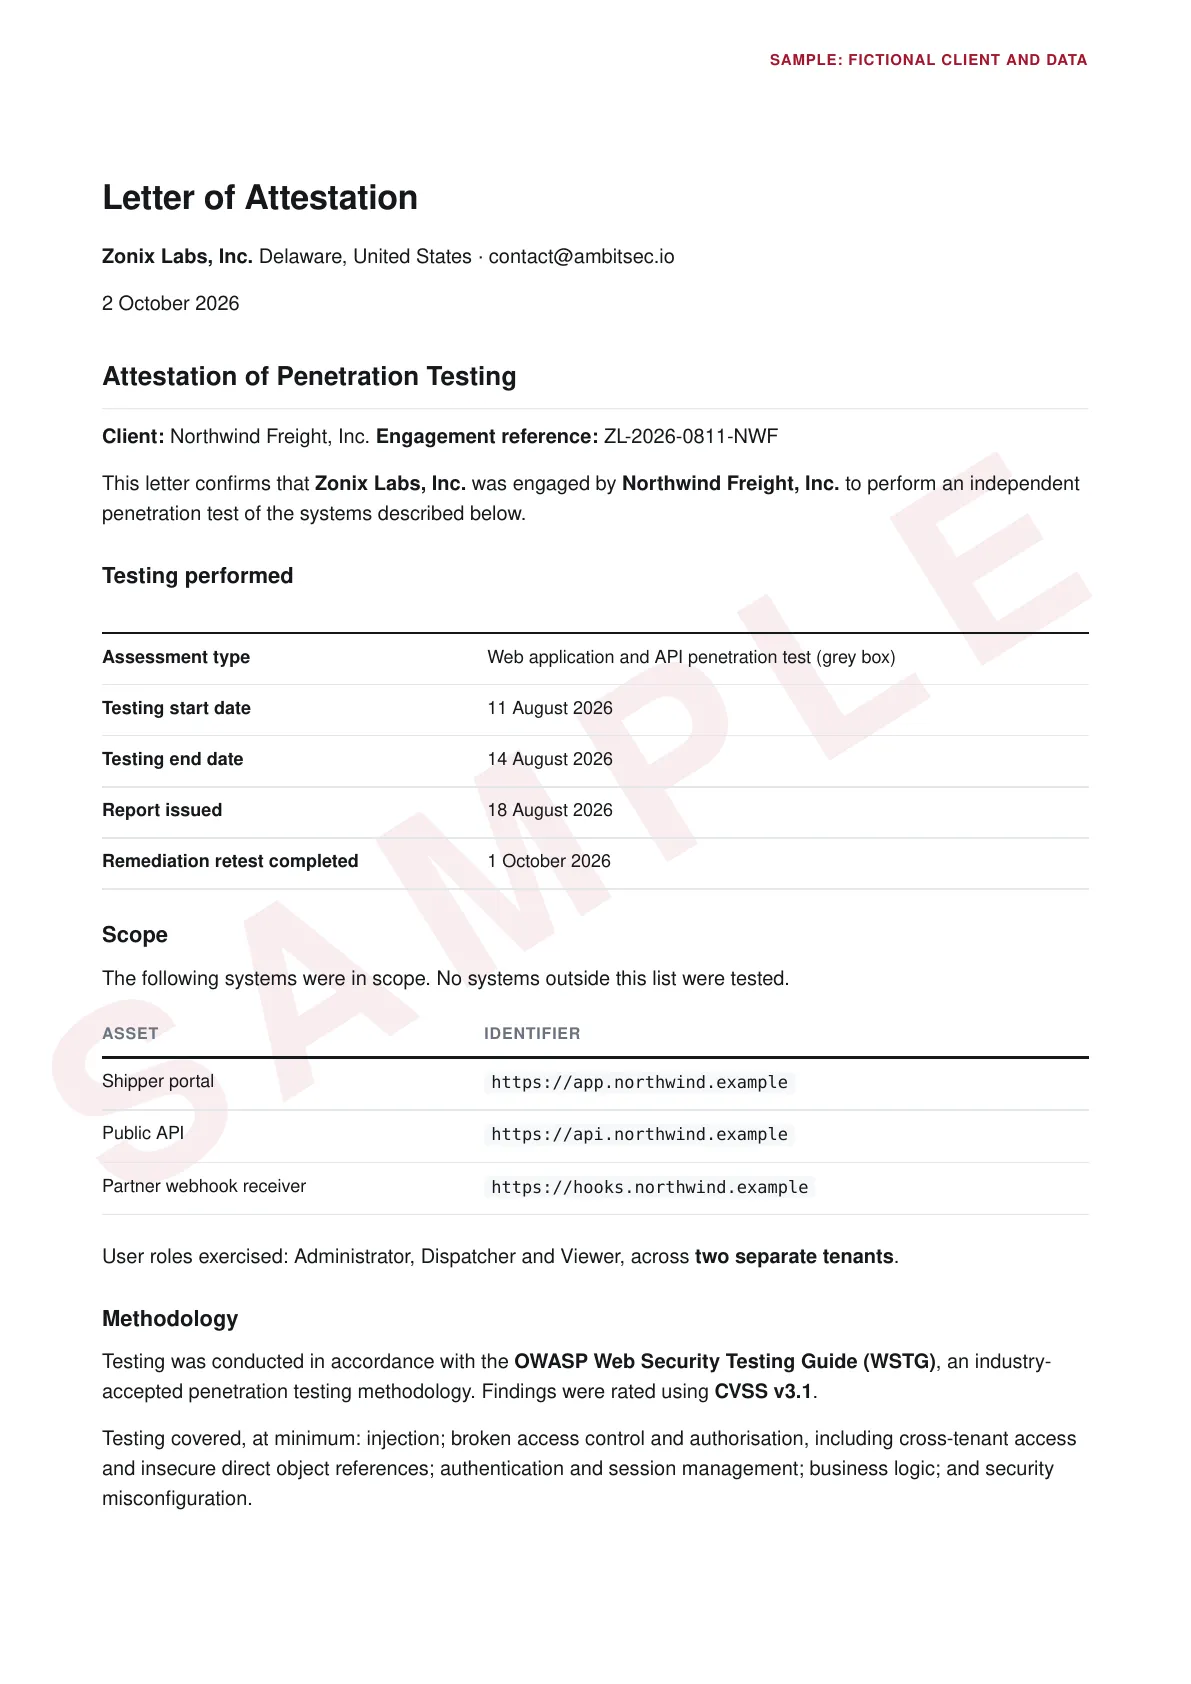
PDF · 2 pages · Sample
Attestation letter
What auditors and customers ask for: scope, dates, methodology, the tester's credentials and the outcome after the retest, signed, with no findings disclosed.
Open the sample letterThe company, people, findings and data in the samples are fictional. Names of testers are replaced by their role; real reports name the pentester who signs them.
For auditors
What auditors look for, and where it is.
Ambit reports are built to be used as evidence for SOC 2, ISO 27001, PCI DSS and HIPAA audits, and for customer security reviews. Your auditor decides what they accept, so confirm the scope with them before testing.
| What they need | What the documents give them | Where |
|---|---|---|
| Scope and dates | Every asset tested, the roles and tenants used, what was out of scope, and the testing window. | Report 1.4, 1.6 |
| Methodology | OWASP WSTG, CVSS v3.1 scoring, and how the agent and the lead pentester worked together. | Report Appendix A |
| Tester credentials | The pentester who led the test, their certification, and their independence from you. | Report 1.3, letter |
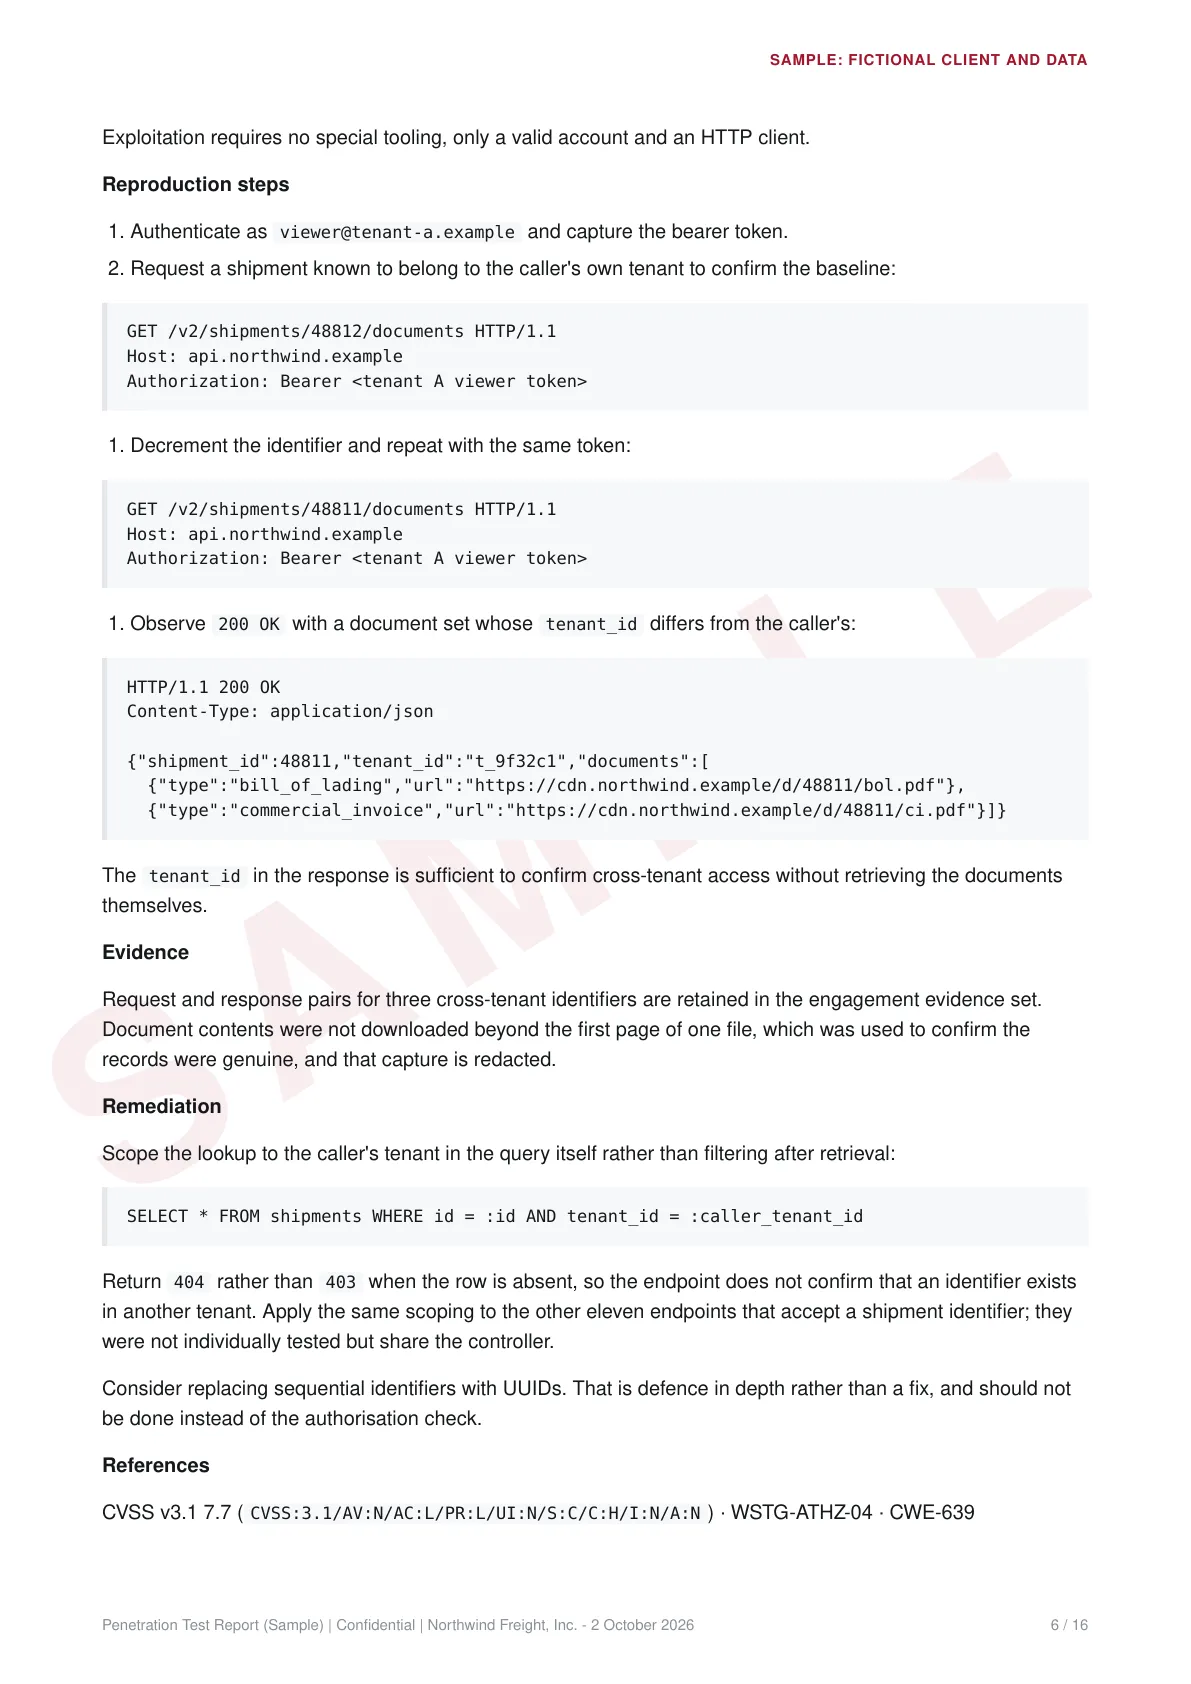
| Findings with evidence | CVSS score and vector, affected routes, evidence, steps to reproduce and remediation. | Report 3 |
| Coverage | Which vulnerability classes were tested, not only what was found. | Report Appendix B |
| Retest results | Each finding marked fixed, open or accepted as risk after the retest. | Report 3, retest report |
| Compliance mapping | Where the report evidences SOC 2 CC4.1 and CC7.1, and ISO 27001 A.8.8 and A.8.29. | Report Appendix C |
| Attestation | One signed page that proves the test happened, without disclosing findings. | Letter |
Every test
Five documents, each for its reader.
Penetration test report
Engineers and auditors
The full report: scope, limitations, executive summary, every finding with evidence, methodology, coverage and the compliance mapping. Released encrypted.
Attestation letter
Auditors, customers, insurers
One signed page: what was tested, when, how and by whom, and the outcome. No findings disclosed, so it can be shared.
Executive summary
Leadership
One or two pages: posture, counts by severity and state, and the findings that matter.
Customer summary
Your customers' security reviewers
Scope, method, outcome and coverage, with nothing exploitable in it.
Retest report
Everyone above, after you fix
What is fixed, what is still open, what you accepted as risk, and anything new since the last report.
Verifiable by anyone
Every Ambit report carries a reference you can check here. Enter it, or drop the PDF in, to confirm the copy is exactly what was signed.
Signed deliverables are kept for 6 years, so a reference stays checkable for as long as an auditor might ask about it.
Get started
Your next pentest, in days.
Tell us what to test. A certified pentester leads the engagement, the agent does the legwork, and you get a signed report your auditor can use.
Fixed price. Results in days. Retest included.